SpringSecurity
前置知识
1、掌握Spring框架
2、掌握SpringBoot使用
3、掌握JavaWeb技术
SpringSecurity简介
概要
Spring 是非常流行和成功的 Java 应用开发框架,Spring Security 正是 Spring 家族中的成员。Spring Security 基于 Spring 框架,提供了一套 Web 应用安全性的完整解决方案。
正如你可能知道的关于安全方面的两个主要区域是“认证”和“授权”(或者访问控制),一般来说,Web 应用的安全性包括用户认证(Authentication)和用户授权 **(Authorization)**两个部分,这两点也是 Spring Security 重要核心功能。
- 用户认证指的是:验证某个用户是否为系统中的合法主体,也就是说用户能否访问该系统。用户认证一般要求用户提供用户名和密码。系统通过校验用户名和密码来完成认证过程。通俗点说就是系统认为用户是否能登录
- 用户授权指的是验证某个用户是否有权限执行某个操作。在一个系统中,不同用户所具有的权限是不同的。比如对一个文件来说,有的用户只能进行读取,而有的用户可以进行修改。一般来说,系统会为不同的用户分配不同的角色,而每个角色则对应一系列的权限。通俗点讲就是系统判断用户是否有权限去做某些事情。
同款产品对比
SpringSecurity
Spring 技术栈的组成部分。
通过提供完整可扩展的认证和授权支持保护你的应用程序
http://spring.io/projects/spring-security
SpringSecurity的特点:
和 Spring 无缝整合。
全面的权限控制。
专门为Web 开发而设计。
旧版本不能脱离Web 环境使用。
新版本对整个框架进行了分层抽取,分成了核心模块和Web 模块。单独引入核心模块就可以脱离Web 环境。
重量级。
Shiro
Apache 旗下的轻量级权限控制框架。
特点:
- 轻量级。Shiro主张的理念是把复杂的事情变简单,针对性能又更高要求的互联网应用又更好的表现
- 通用性
- 好处:不局限于Web环境,可以脱离Web环境
- 缺点:在Web环境下一些特定的需求需要手动编写代码制定
Security 是 Spring 家族中的一个安全管理框架,实际上,在 Spring Boot 出现之前,Spring Security 就已经发展了多年了,但是使用的并不多,安全管理这个领域,一直是 Shiro 的天下。
相对于 Shiro,在 SSM 中整合 Spring Security 都是比较麻烦的操作,所以,Spring Security 虽然功能比 Shiro 强大,但是使用反而没有 Shiro 多(Shiro 虽然功能没有Spring Security 多,但是对于大部分项目而言,Shiro 也够用了)。
自从有了 Spring Boot 之后,Spring Boot 对于 Spring Security 提供了自动化配置方案,可以使用更少的配置来使用 Spring Security。
因此,一般来说,常见的安全管理技术栈的组合是这样的:
- SSM + Shiro
- SpringBoot/Spring Cloud + SpringSecurity
SpringSecurity入门程序
创建SpringBoot工程
引入spring-security的依赖
<dependency> <groupId>org.springframework.boot</groupId> <artifactId>spring-boot-starter-security</artifactId> </dependency> 12345678910111213141516171819- 编写controller类 - ```java package com.raehp.controller; import org.springframework.web.bind.annotation.GetMapping; import org.springframework.web.bind.annotation.RequestMapping; import org.springframework.web.bind.annotation.RestController; @RestController @RequestMapping("/test") public class HelloSecurity { @GetMapping("/hello") public String hello() { return "Hello Security!"; } }1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
- 访问localhost:8080/test/hello
- 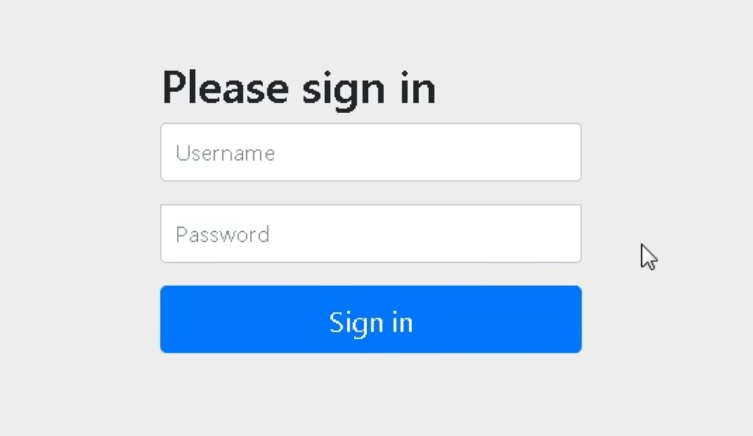
默认用户名为:user
密码为:每运行一次 随机生成一个密码
# SpringSecurity基本原理
SpringSecurity 本质是一个过滤器链:
从启动是可以获取到过滤器链:
<table><tbody><tr><td class="gutter"><pre><span class="line">1</span><br><span class="line">2</span><br></pre></td><td class="code"><pre><span class="line">org.springframework.security.web.context.request.async.WebAsyncManagerIntegrationFil ter</span><br><span class="line">org.springframework.security.web.context.SecurityContextPersistenceFilter org.springframework.security.web.header.HeaderWriterFilter org.springframework.security.web.csrf.CsrfFilter org.springframework.security.web.authentication.logout.LogoutFilter org.springframework.security.web.authentication.UsernamePasswordAuthenticationFilter org.springframework.security.web.authentication.ui.DefaultLoginPageGeneratingFilter org.springframework.security.web.authentication.ui.DefaultLogoutPageGeneratingFilter org.springframework.security.web.savedrequest.RequestCacheAwareFilter org.springframework.security.web.servletapi.SecurityContextHolderAwareRequestFilter org.springframework.security.web.authentication.AnonymousAuthenticationFilter org.springframework.security.web.session.SessionManagementFilter org.springframework.security.web.access.ExceptionTranslationFilter org.springframework.security.web.access.intercept.FilterSecurityInterceptor</span><br></pre></td></tr></tbody></table>
代码底层流程:重点看三个过滤器:
- **FilterSecurityInterceptor:**是一个方法级的权限过滤器, 基本位于过滤链的最底部。
- ```
public void invoke(FilterInvocation filterInvocation) throws IOException, ServletException {
if (this.isApplied(filterInvocation) && this.observeOncePerRequest) {
filterInvocation.getChain().doFilter(filterInvocation.getRequest(), filterInvocation.getResponse());
} else {
if (filterInvocation.getRequest() != null && this.observeOncePerRequest) {
filterInvocation.getRequest().setAttribute("__spring_security_filterSecurityInterceptor_filterApplied", Boolean.TRUE);
}
InterceptorStatusToken token = super.beforeInvocation(filterInvocation);
try {
filterInvocation.getChain().doFilter(filterInvocation.getRequest(), filterInvocation.getResponse());
} finally {
super.finallyInvocation(token);
}
super.afterInvocation(token, (Object)null);
}
}
1234567891011121314151617181920212223242526272829303132333435363738 - super.beforeInvocation(fi) 表示查看之前的 filter 是否通过。 - fi.getChain().doFilter(fi.getRequest(), fi.getResponse());表示真正的调用后台的服务。- **ExceptionTranslationFilter:**是个异常过滤器,用来处理在认证授权过程中抛出的异常 - ```java public void doFilter(ServletRequest request, ServletResponse response, FilterChain chain) throws IOException, ServletException { this.doFilter((HttpServletRequest)request, (HttpServletResponse)response, chain); } private void doFilter(HttpServletRequest request, HttpServletResponse response, FilterChain chain) throws IOException, ServletException { try { chain.doFilter(request, response); } catch (IOException var7) { IOException ex = var7; throw ex; } catch (Exception var8) { Exception ex = var8; Throwable[] causeChain = this.throwableAnalyzer.determineCauseChain(ex); RuntimeException securityException = (AuthenticationException)this.throwableAnalyzer.getFirstThrowableOfType(AuthenticationException.class, causeChain); if (securityException == null) { securityException = (AccessDeniedException)this.throwableAnalyzer.getFirstThrowableOfType(AccessDeniedException.class, causeChain); } if (securityException == null) { this.rethrow(ex); } if (response.isCommitted()) { throw new ServletException("Unable to handle the Spring Security Exception because the response is already committed.", ex); } this.handleSpringSecurityException(request, response, chain, (RuntimeException)securityException); }
**UsernamePasswordAuthenticationFilter :**对/login 的 POST 请求做拦截,校验表单中用户名,密码。
public Authentication attemptAuthentication(HttpServletRequest request, HttpServletResponse response) throws AuthenticationException {
        if (this.postOnly && !request.getMethod().equals("POST")) {
            throw new AuthenticationServiceException("Authentication method not supported: " + request.getMethod());
        } else {
            String username = this.obtainUsername(request);
            username = username != null ? username : "";
            username = username.trim();
            String password = this.obtainPassword(request);
            password = password != null ? password : "";
            UsernamePasswordAuthenticationToken authRequest = new UsernamePasswordAuthenticationToken(username, password);
            this.setDetails(request, authRequest);
            return this.getAuthenticationManager().authenticate(authRequest);
        }
    }
123456789101112131415161718    ## UserDetailService接口详解当什么也没有配置的时候,账号和密码是由 Spring Security 定义生成的。而在实际项目中账号和密码都是从数据库中查询出来的。 所以我们要通过自定义逻辑控制认证逻辑。 如果需要自定义逻辑时,只需要实现 UserDetailsService 接口即可。接口定义如下:```javapackage org.springframework.security.core.userdetails;public interface UserDetailsService {    UserDetails loadUserByUsername(String username) throws UsernameNotFoundException;}
返回值:UserDetails
这个类是系统默认的用户“主体”
1 | // 表示获取登录用户所有权限 |
UserDetails实现类
1 | package org.springframework.security.core.userdetails; |
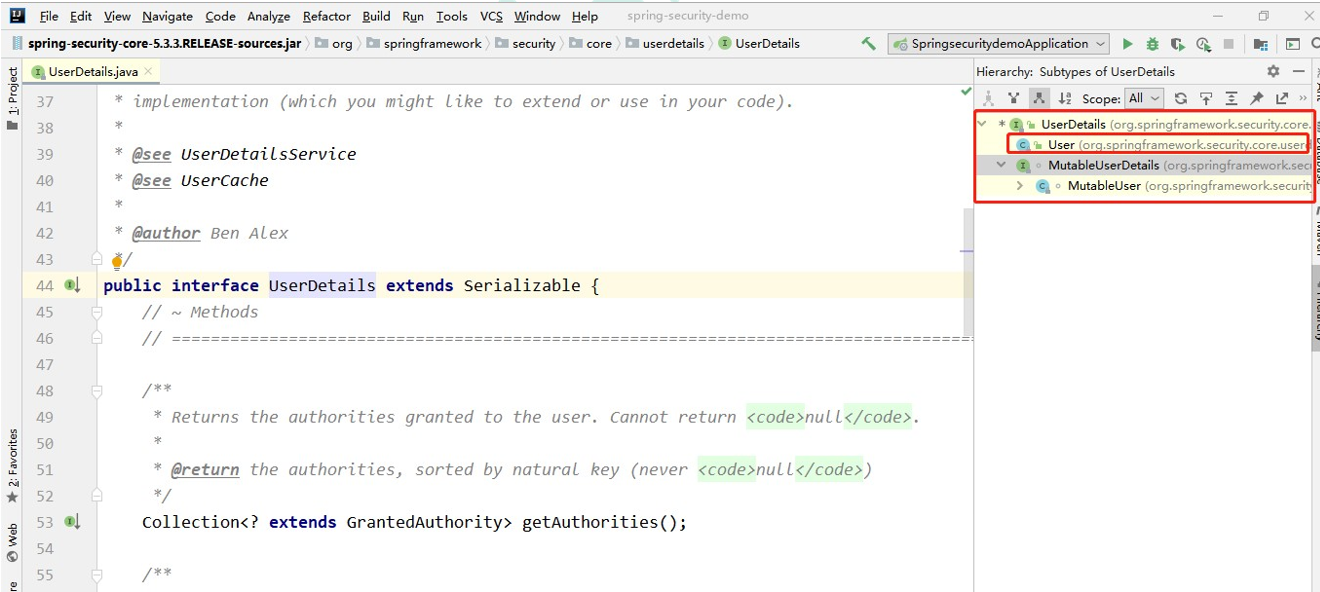
以后我们只需要使用 User 这个实体类即可!
1 | public User(String username, String password, Collection<? extends GrantedAuthority> authorities) { |
- 方法参数username:
- 表示用户名。此值是客户端表单传递过来的数据。默认情况下必须叫 username,否则无法接收。
步骤总结:
- 创建类继承UsernamePassowrdAuthenticationFilter,重写三个方法
- 创建类实现UserDetailService,编写查询数据过程,返回User对象
这个User对象是安全框架提供对象
PasswordEncoder接口讲解
1 | // 表示把参数按照特定的解析规则进行解析 |
接口实现类:
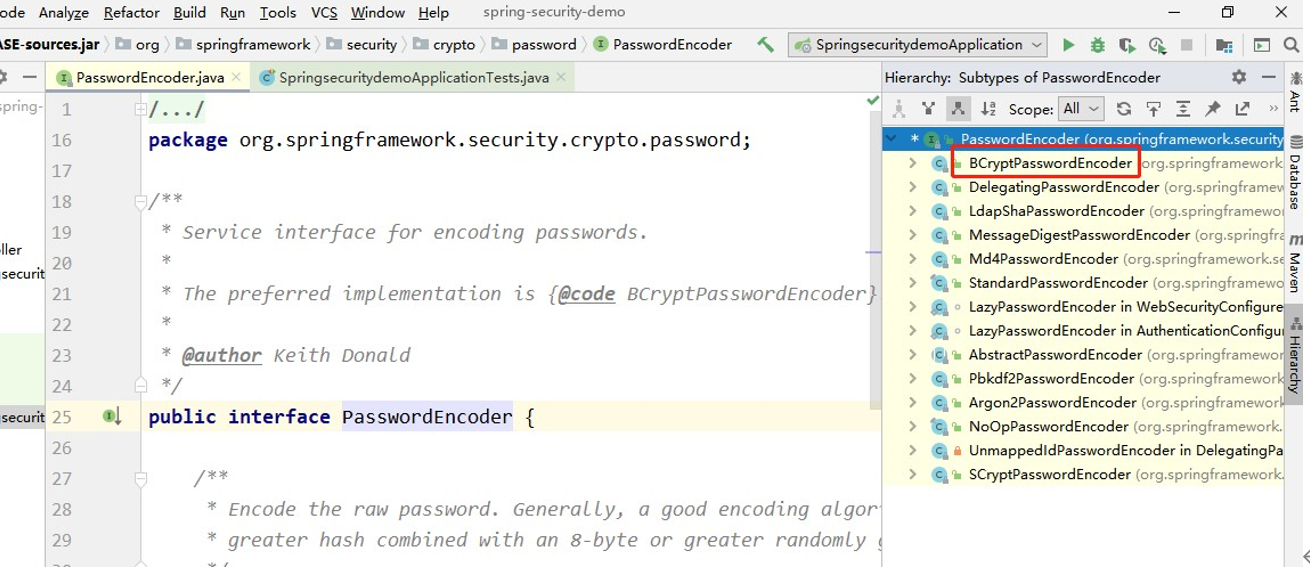
BCryptPasswordEncoder 是 Spring Security 官方推荐的密码解析器,平时多使用这个解析器。
BCryptPasswordEncoder 是对bcrypt 强散列方法的具体实现。是基于 Hash 算法实现的单向加密。可以通过 strength 控制加密强度,默认10.
方法演示:
1 |
|
SpringBoot对Security的自动配置
https://docs.spring.io/spring- security/site/docs/5.3.4.RELEASE/reference/html5/#servlet-hello
Web权限方案
设置Security密码
以下有三种方式可以配置username和password
- 通过配置文件
- 通过配置类
- 自定义编写实现类
通过配置文件
创建application.properties文件
1 | spring.security.user.name=raehp |
运行启动类 访问controller 测试
通过配置类
创建securitConfig配置类 标注@Configuration注解 让其继承 WebSecurityConfigurerAdapter类
并实现其中的configure方法
1 | package com.raehp.config; |
访问控制层,输入账户密码验证通过
自定义编写实现类
- 第一步、创建配置类,设置使用哪个userDetailService实现类
- 第二步、编写实现类,返回User对象,User对象有用户名密码和操作权限
创建配置类
1 | package com.raehp.config; |
编写实现类 创建 service/MyUserService 接口
1 | package com.raehp.service; |
运行访问controller、测试通过
连接数据库
- 引入相关依赖
- 创建数据库和表
- 创建对应的实体类
- 整合mybatis-plus,创建mapper接口 实现BaseMapper接口
- 在MyUserDetailService中调用mapper中的方法查询函数
- 数据库配置
一、引入相关依赖
1 | <!--mybatis-plus--> |
二、创建数据库和表
1 | create table users( |
三、创建实体类
1 | package com.raehp.pojo; |
四、创建mapper接口使其继承BaseMapper接口
1 | package com.raehp.mapper; |
五、在MyUserDetailService中调用mapper中的方法查询函数
1 | package com.raehp.service; |
六、数据库配置
1 | spring.datasource.driver-class-name=com.mysql.cj.jdbc.Driver |
自定义登录页面
- 编写配置类
- 创建相关文件
第一步、在配置类实现相关配置
1 |
|
第二步、创建相关的页面 static/login.html
1 |
|
1 | package com.atguigu.securitydemo1.controller; |
第三步、访问localhost:8081/test/hello 不会被拦截
访问localhost:8081/test/index 会跳转到login.html 页面 输入账户密码 登陆成功后 会访问到 /test/index
基于角色或权限进行访问控制
hasAuthority方法
如果当前的主题具有指定的权限,则返回true,否则返回false(只针对某一个权限)
1 | 1. 在配置类设置当前访问地址有哪些权限 |
没有权限 访问后会返回**(type = “forbidden” status=”403”)**
hasAnyAuthority方法
如果当前的主题有任何提供的角色(给定的作为一个逗号分割的字符串列表)的话,返回true
1 | 1. 在配置类设置当前访问地址有哪些权限 |
hasRole方法
如果用户具备给定角色就允许访问,否则出现403,如果当前主体具有指定的角色,则返回true
1 | 1. 在配置类设置当前访问地址那些角色可以访问 |
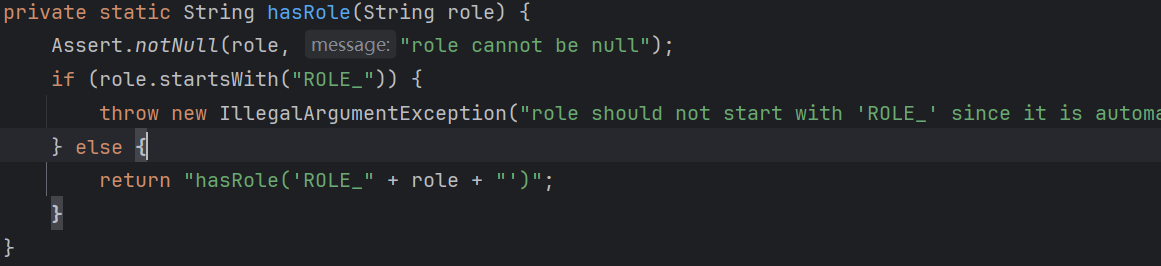
注意:这里给User -> role权限时 要加 ROLE_ 这是因为源码中自动帮我们添加了
hasAnyRole方法
用户具备任意一个条件即可访问
1 | 1. 在配置类设置当前访问地址那些角色可以访问 |
自定义403页面
1 | 在自定义配置中配置 |
注解使用
@Secured
用户具有某个角色,可以访问方法
- 在启动类(或配置类)上添加
@EnableGlobalMethodSecurity(securedEnabled=true) - 在controller上添加
@Secured注解设置角色 - userDetailService方法设置当前登录用户角色
第一步、@EnableGlobalMethodSecurity(securedEnabled=true)
1 | package com.atguigu.securitydemo1; |
第二步、@Secured
1 |
|
第三步、userDetailService设置登录用户权限
1 | List<GrantedAuthority> auths = |
@PreAuthorize
方法执行之前校验
- 在启动类(或配置了)上添加
@EnableGlobalMethodSecurity(prePostEnabled = true) - 在controller方法上添加PreAuthorize方法,可以将登录用户的 roles/permissions 参数传到方法中。
第一步、@EnableGlobalMethodSecurity(prePostEnabled = true)
1 | package com.atguigu.securitydemo1; |
第二步、@PreAuthorize
1 |
|
@PostAuthorize
方法执行后校验
- 在启动类(或配置了)上添加
@EnableGlobalMethodSecurity(prePostEnabled = true) - 在controller方法上添加
@PostAuthorize注解,注解使用并不多,在方法执行后再进行权限验证,适合验证带有返回值的权限.
第一步、@EnableGlobalMethodSecurity(prePostEnabled = true)
1 | package com.atguigu.securitydemo1; |
第二步、@PostAuthorize
1 |
|
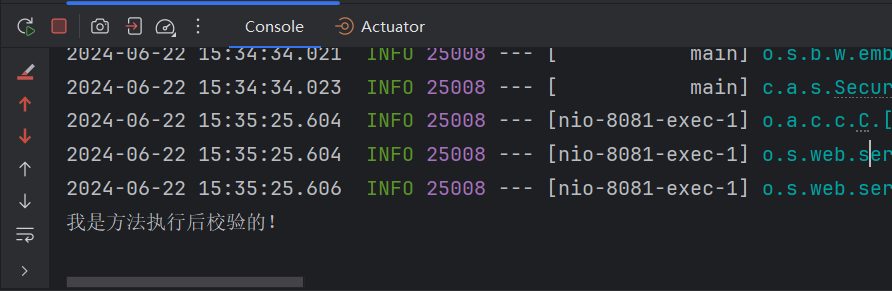
当我们访问这个请求并且提交后 会出现以下情况:
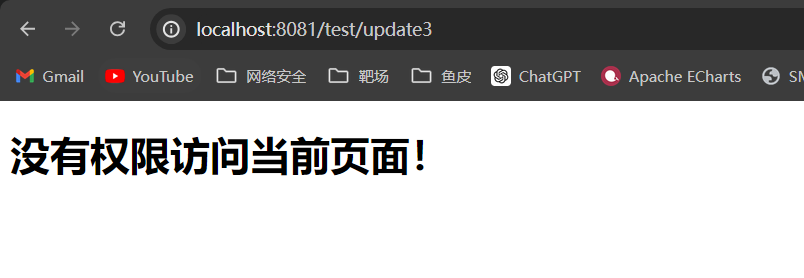
没有权限访问,但是我们打开控制台发现 方法已经执行完毕
@PostFilter
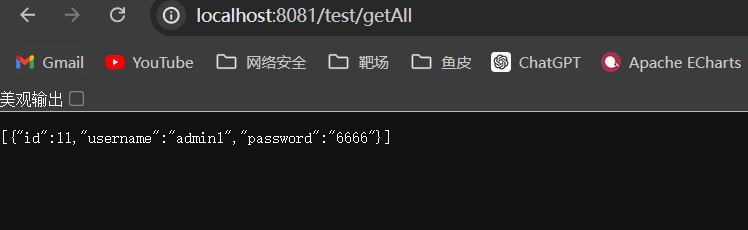
权限验证之后对数据进行过滤
- 表达式中的 filterObject 引用的是方法返回值List 中的某一个元素
1 |
|
结果如下:
@PreFilter
进入控制器之前对数据进行过滤
1 |
|
用户注销
创建一个登录成功的页面 success.html
1 |
|
在securityConfig中添加如下配置
1 | // 退出url,退出成功后跳转的页面 |
更新securityConfig 中登录成功后跳转的页面为success.html
1 | .defaultSuccessUrl("/success.html").permitAll() // 登录成功后,跳转路径 |
类似于浏览器中的session
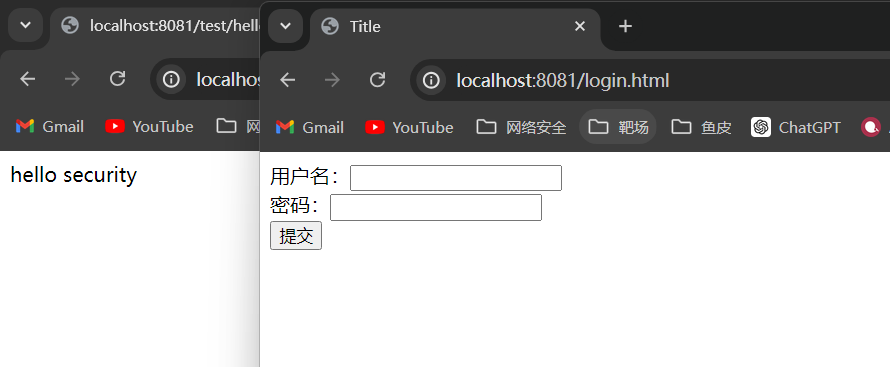
当我们登陆成功后,可以访问别的页面,但是当我们退出后就不能访问其他页面了
退出之前:
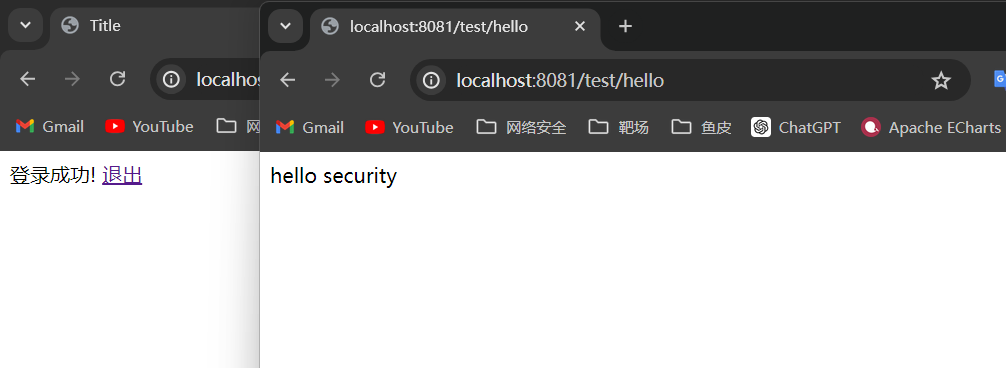
退出之后:
基于数据库设置记住我
第一步、创建数据库表(也可以不创建,设置配置文件时 可以帮我们创建)
1 | CREATE TABLE `persistent_logins` ( |
第二步、设置数据库配置文件
1 | #mysql数据库配置 |
第三步、在安全配置类中编写数据库配置类
1 | // 注入数据源 |
第四步、修改安全配置类
1 | http.formLogin() |
第五步、页面中设置记住密码复选框
1 |
|
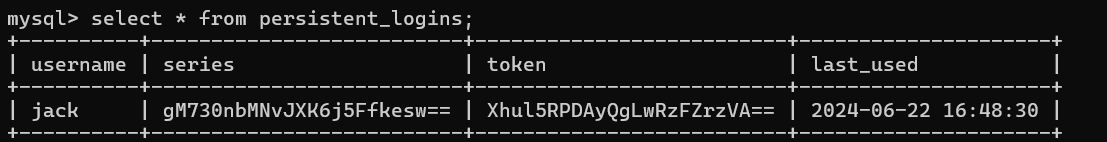
测试 查询数据库
CSRF
跨站请求伪造(英语:Cross-site request forgery),也被称为 one-click attack 或者 session riding,通常缩写为 CSRF 或者 XSRF, 是一种挟制用户在当前已
登录的 Web 应用程序上执行非本意的操作的攻击方法。跟跨网站脚本(XSS)相比,XSS 利用的是用户对指定网站的信任,CSRF 利用的是网站对用户网页浏览器的信任。
跨站请求攻击,简单地说,是攻击者通过一些技术手段欺骗用户的浏览器去访问一个自己曾经认证过的网站并运行一些操作(如发邮件,发消息,甚至财产操作如转账和购买商品)。由于浏览器曾经认证过,所以被访问的网站会认为是真正的用户操作而去运行。这利用了web 中用户身份验证的一个漏洞:简单的身份验证只能保证请求发自某个用户的浏览器,却不能保证请求本身是用户自愿发出的。
从 Spring Security 4.0 开始,默认情况下会启用CSRF 保护,以防止CSRF 攻击应用程序,Spring Security CSRF 会针对 PATCH,POST,PUT 和DELETE 方法进行防护。
参考尚硅谷**==SpringSecurity-P19 CSRF==**
SpringSecurity微服务权限方案
什么是微服务
微服务由来
微服务最早由Martin Fowler 与 James Lewis 于 2014 年共同提出,微服务架构风格是一种使用一套小服务来开发单个应用的方式途径,每个服务运行在自己的进程中,并使用轻量级机制通信,通常是 HTTP API,这些服务基于业务能力构建,并能够通过自动化部署机制来独立部署,这些服务使用不同的编程语言实现,以及不同数据存储技术,并保持最低限度的集中式管理。
微服务的优势
(1)微服务每个模块就相当于一个单独的项目,代码量明显减少,遇到问题也相对来说比较好解决。
(2)微服务每个模块都可以使用不同的存储方式(比如有的用 redis,有的用 mysql等),数据库也是单个模块对应自己的数据库。
(3)微服务每个模块都可以使用不同的开发技术,开发模式更灵活。
微服务的本质
(1)微服务,关键其实不仅仅是微服务本身,而是系统要提供一套基础的架构,这种架构使得微服务可以独立的部署、运行、升级,不仅如此,这个系统架构还让微服务与微服务之间在结构上“松耦合”,而在功能上则表现为一个统一的整体。这种所谓的“统一的整体”表现出来的是统一风格的界面,统一的权限管理,统一的安全策略,统一的上线过 程,统一的日志和审计方法,统一的调度方式,统一的访问入口等等。
(2)微服务的目的是有效的拆分应用,实现敏捷开发和部署。